
Cisco is aware of and is working on what products could end up affected by the Ripple 20 vulnerabilities on the Treck IP stack implementation which could result in remote code execution, denial of service (DoS), or information disclosure, depending on the specific vulnerability.
Cisco is investigating its product line to determine which products may be affected by these vulnerabilities it listed as critical. As the investigation progresses, Cisco said it will release updates.
The following products are under active investigation to determine whether they are affected by the vulnerabilities:
- Cisco ASR 5000 Series Routers
- Cisco Home Node-B Gateway
- Cisco IP Services Gateway (IPSG)
- Cisco PDSN/HA Packet Data Serving Node and Home Agent
In its advisory, Cisco did release a list of products affected by the issue. The product are:

- Cisco GGSN Gateway GPRS Support Node
- Cisco MME Mobility Management Entity
- Cisco PGW Packet Data Network Gateway
- Cisco System Architecture Evolution Gateway (SAEGW)
Cisco is currently working on fixes and workarounds to handle any issues affiliated with the vulnerabilities.
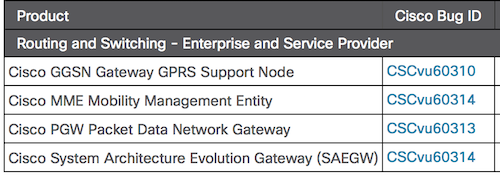
Cisco products affected by Ripple 20.
In all cases, Cisco said users should upgrade devices to ensure they contain sufficient memory and confirm current hardware and software configurations will continue to be supported properly by the new release.
The Cisco Product Security Incident Response Team (PSIRT) said it is not aware of any malicious use of the vulnerabilities.
In addition to the Ripple 20 details, Cisco also released security updates to address vulnerabilities affecting multiple products where a remote attacker could take control of an affected system.
The following are Cisco advisories for its various products:
- Webex Meetings and Cisco Webex Meetings Server Token Handling Unauthorized Access Vulnerability
- Webex Meetings Desktop App URL Filtering Arbitrary Program Execution Vulnerability
- Webex Meetings Desktop App for Mac Update Feature Code Execution Vulnerability
- TelePresence Collaboration Endpoint and RoomOS Software Command Injection Vulnerability
- Small Business RV Series Routers Stack Overflow Arbitrary Code Execution Vulnerabilities
- Small Business RV110W, RV130, RV130W, and RV215W Series Routers Management Interface Vulnerabilities
- Small Business RV Series Routers Command Injection Vulnerabilities
Click here for the entire list of Cisco security advisories.