
Cisco has a fix available to handle a vulnerability in the web services interface of Cisco Adaptive Security Appliance (ASA) Software and Cisco Firepower Threat Defense (FTD) Software that could allow an unauthenticated, remote attacker to conduct directory traversal attacks and read sensitive files on a targeted system.
Cisco has become aware of public exploit code and active exploitation of the vulnerability, which means users should patch or upgrade as soon as possible.
The vulnerability, which Cisco rated high and has a CVSS score of 7.5, is because there is a lack of proper input validation of URLs in HTTP requests processed by an affected device.
An attacker could exploit this vulnerability by sending a crafted HTTP request containing directory traversal character sequences to an affected device. A successful exploit could allow the attacker to view arbitrary files within the web services file system on the targeted device.

The web services file system ends up enabled when the affected device is configured with either WebVPN or AnyConnect features. This vulnerability does not lead to access to ASA or FTD system files or underlying operating system (OS) files.
While Cisco did release updates, there are no workarounds that address this vulnerability.
This vulnerability affects Cisco products if they are running a vulnerable release of Cisco ASA Software or Cisco FTD Software with a vulnerable AnyConnect or WebVPN configuration.
In the table below, the left column lists the Cisco ASA features that are vulnerable. The right column indicates the basic configuration for the feature from the show running-config CLI command. If the device is configured for one of these features, it is vulnerable.
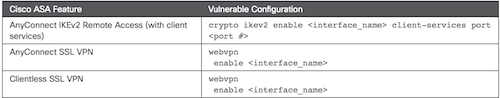
The left column lists the vulnerable Cisco ASA features. The right column indicates the basic configuration for the feature from the show running-config CLI command. If the device is configured for one of these features, it is vulnerable.
Source: Cisco
On devices running Cisco FTD Software, the show running-config command is available from Diagnostic CLI mode only. To enter Diagnostic CLI mode, use the system support diagnostic-cli command in the regular Firepower Threat Defense CLI.
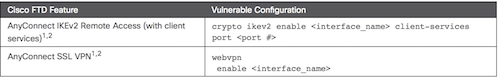
The left column lists the vulnerable Cisco FTD features. The right column indicates the basic configuration for the feature from the show running-config CLI command. If the device is configured for one of these features, it is vulnerable.
Source: Cisco
The attacker can view files within the web services file system only. The web services file system is enabled for the WebVPN and AnyConnect features. The web services files the attacker can view may have information such as WebVPN configuration, bookmarks, web cookies, partial web content, and HTTP URLs.
To help detect and/or block attempts to exploit the vulnerability, users who use the SSL Decryption feature for affected traffic on Cisco Firepower sensors can enable Snort rules 54598 through 54601, from SRU number 2020-07-22-001, by using the Cisco Firepower Management Center.